
Cybersecurity architecture
Defense-in-depth, segmentation, firewall security, identity, secure connectivity, monitoring, and resilient infrastructure.
Synapse Cyber was created to help organizations connect technical security, governance, AI adoption, and business risk in one practical advisory model.
Shahriar Hatami brings more than two decades of technology experience, including cybersecurity architecture, infrastructure engineering, enterprise security controls, risk management, and operational resilience.
His work spans both strategic and technical layers: translating risk into priorities, designing secure architectures, strengthening governance, and implementing controls that can be operated and measured in real environments.
Today, that experience is extended into AI governance and AI automation—helping organizations adopt AI responsibly while maintaining security, accountability, human oversight, and business value.
Defense-in-depth, segmentation, firewall security, identity, secure connectivity, monitoring, and resilient infrastructure.
SIEM, detection, MITRE ATT&CK-aligned visibility, vulnerability management, incident readiness, and security telemetry.
NIST, CIS, ISO 27001, compliance, risk treatment, evidence, executive reporting, and governance operating models.
AI risk, policy, human oversight, workflow automation, AI agents, n8n orchestration, and responsible adoption.
Selected areas of experience that shape the way Synapse Cyber approaches advisory work.
Long-term experience with mission-critical infrastructure, networking, identity, routing, high availability, and enterprise systems.
Hands-on deployment and architecture of layered security controls including IPS/IDS, antivirus, application control, DPI-SSL, DNS security, segmentation, and secure access.
Designing security visibility, dashboards, alerting, configuration assessment, vulnerability monitoring, and operational detection workflows.
Connecting technical controls to governance frameworks, gap analysis, policy, evidence, remediation tracking, and executive oversight.
Building practical approaches to AI inventory, policy, risk assessment, accountability, oversight, evidence, and lifecycle governance.
Using workflow automation and AI to streamline project management, assessments, reporting, approvals, operational processes, and business workflows.
Selected credentials supporting Synapse Cyber's cybersecurity, governance, audit, and risk-management capabilities.
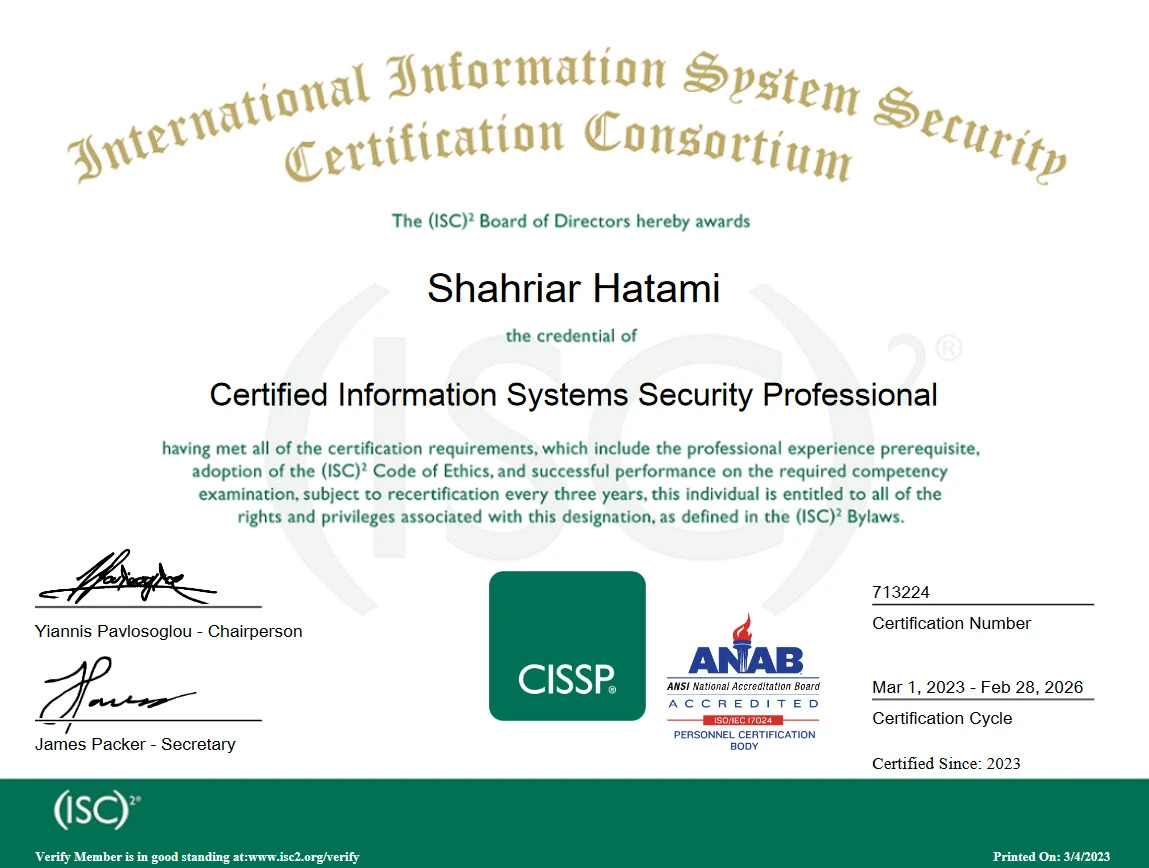
Certified since 2023. The credential recognizes advanced cybersecurity experience and competency across the CISSP body of knowledge.
View certificate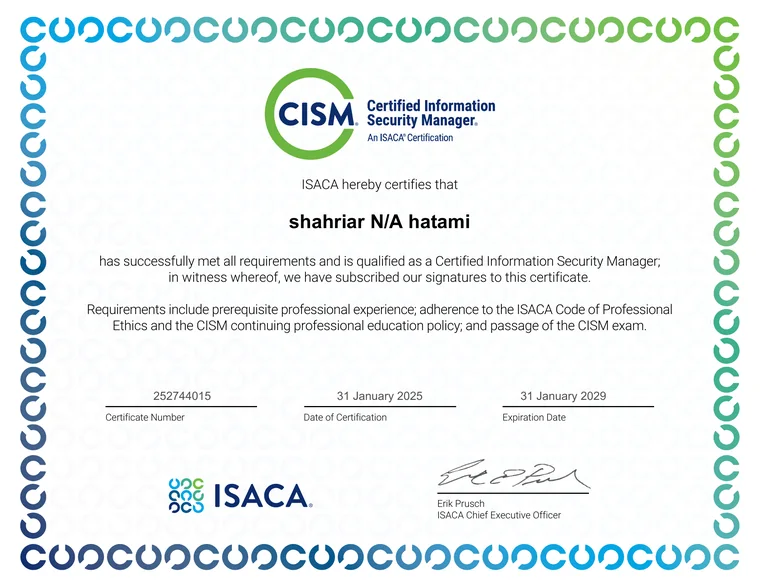
Certified January 31, 2025. The certificate lists an expiration date of January 31, 2029.
View certificate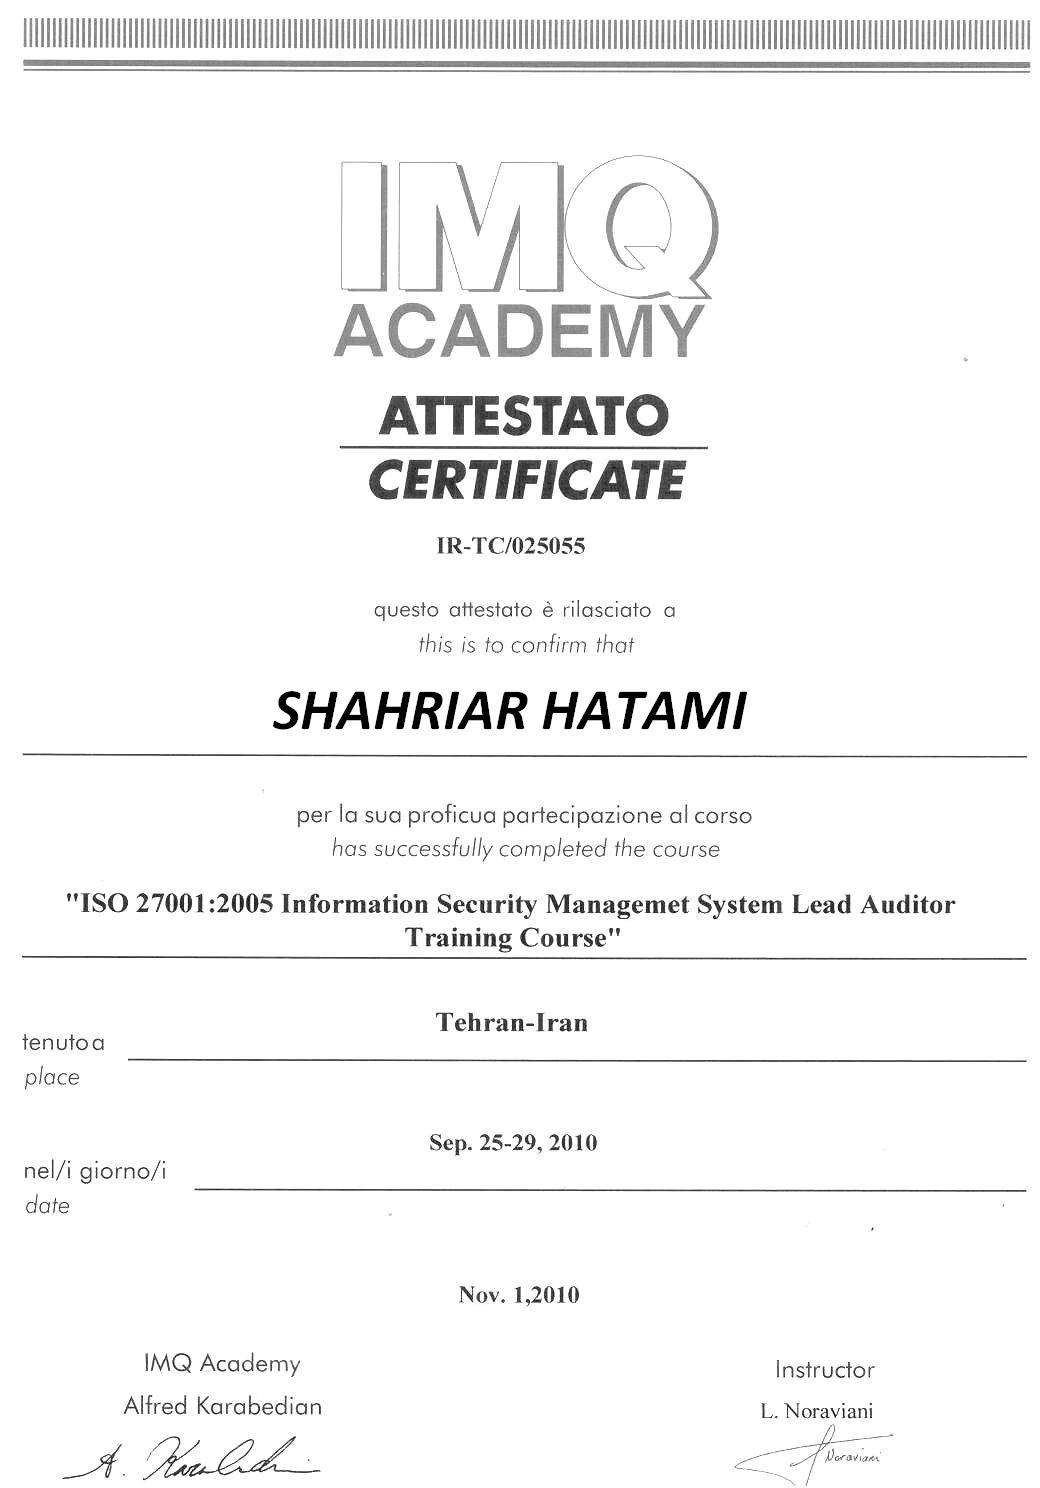
Completed the ISO 27001:2005 Information Security Management System Lead Auditor Training Course in 2010.
View certificateCertificates are displayed for professional background and transparency. Credential status should be verified directly with the issuing organization when required.
The goal is to make security and governance easier to understand, prioritize, implement, and maintain.
Start with the organization, business objective, environment, and actual risk context.
Focus resources on the controls, risks, and improvements that create meaningful value.
Use AI and automation to accelerate work while preserving review, accountability, and approval.
Connect recommendations to owners, evidence, outcomes, risk reduction, and recurring oversight.
Start with a conversation, a readiness tool, or a structured assessment.